

What Is Proxy Chaining? Can Static Residential IPs Be Chained?


Clean IP picks: Static IPs from $1.5 each, Dynamic IPs from $0.5/GB


In multi-account management, cross-border business, and large-scale data collection, network requests may sometimes need to pass through multiple proxy nodes before reaching the target website. This is where a common network architecture comes in: proxy chaining.
How does proxy chaining work? Can a static residential IP be added to a proxy chain? What impact does it have? Let's take a closer look.
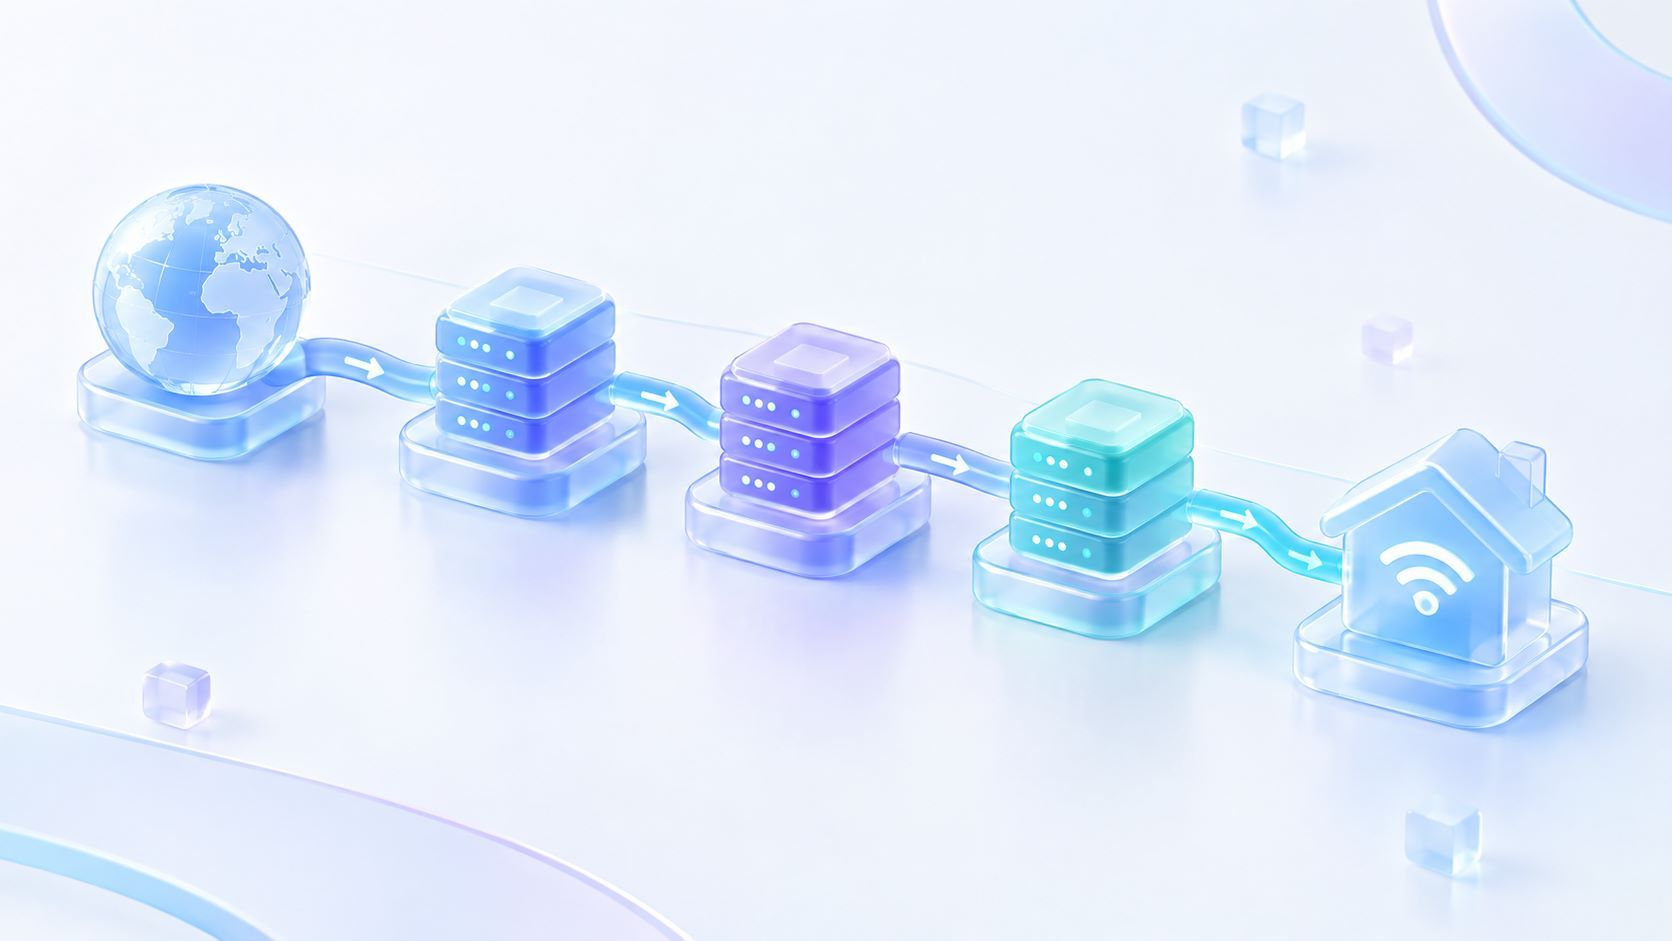
What Is Proxy Chaining
Proxy chaining connects multiple proxy servers in sequence, allowing traffic to pass through each proxy before reaching the target website.
A standard proxy connection looks like this:
Client → Proxy Server → Target Website
A proxy chain looks like this:
Client → Proxy Node A → Proxy Node B → Target Website
In a multi-level setup, each proxy mainly establishes a connection with the next node rather than connecting directly to the target website. This creates some separation between the connection information visible to different nodes.
However, what each node can see depends on the proxy protocol, configuration, authentication method, and implementation. There is no guarantee that every node will be unable to see the full path.
For standard HTTP/HTTPS requests, the network exit IP seen by the target website is usually the IP address of the last hop.
However, websites can also use signals such as TLS fingerprints, browser characteristics, and request behavior to evaluate a connection. The IP address is only one factor.
Pros and Cons of Proxy Chaining
There are two main advantages:
▸ Layered architecture: Access, relay, and exit nodes can be configured separately, allowing each layer to be adjusted independently. Changing a relay node does not require changing the exit IP.
▸ Controlled exit: With a fixed exit node at the end of the chain, the target website consistently sees the same IP address.
The drawbacks are just as clear:
▸ Higher latency: More proxy hops usually mean higher network latency because requests have to be relayed between multiple nodes.
▸ More points of failure: If any node in the chain goes down, the connection can fail.
▸ More difficult troubleshooting: When something goes wrong, each node may need to be checked, making troubleshooting more complex than with a single proxy.
A longer chain is not necessarily better. Each additional node increases the complexity of connection setup, data transfer, and troubleshooting.
If an extra relay is not needed, adding one may only reduce speed and stability.
The number of hops should be based on network distance, proxy quality, and business needs rather than a fixed number.
Can a Static Residential IP Be Added to a Proxy Chain?
In practice, a static residential IP is typically used as the last hop in a proxy chain.
The reason is simple: the last hop determines the network exit used to reach the target website for standard HTTP/HTTPS requests.
For standard HTTP/HTTPS requests, the target website usually sees the exit IP of the last hop. If the last hop uses a static residential IP, the request exits through a fixed residential network address.
A static residential IP generally refers to an IP address that remains stable over time and is associated with a residential network.
Data center IPs typically come from cloud providers or hosting facilities. They often offer well-established network infrastructure and good connection performance, but their data center characteristics may also be easier to identify.
One point is worth clarifying: a residential exit does not mean the request comes from a real user. Modern risk-control systems evaluate requests using multiple signals, including network characteristics, TLS fingerprints, and user behavior. A residential IP is only one factor.
Two common setups include:
1. Relay + localized exit: The first hop uses a data center proxy with sufficient bandwidth for forwarding, while the second hop uses a static residential IP in the target country or city as the exit.
2. Front-end relay + dedicated exit: The front-end node handles connection forwarding, while a dedicated static residential IP is used as the exit. This setup is suitable for scenarios that require a fixed and independent network exit.
Before setting up a proxy chain, check three things:
1. Whether the provider supports proxy chaining and whether the proxy nodes can connect to each other properly;
2. Whether the protocols are compatible, including which protocols are supported by the front-end and exit proxies and whether the client supports mixed proxy chaining;
3. Whether the exit IP is dedicated and whether it is fixed to the required country or city.
If you need a static residential IP in a specific country or city, you can choose IP resources based on your target location. IPDEEP static residential IPs are available across multiple regions for use cases that require a fixed network exit.
What Proxy Chaining Cannot Solve
Proxy chaining changes the network path and final exit address, but requests still carry other signals when they reach the target website:
▸ IP and ASN: The IP's network type and reputation history.
▸ TLS fingerprint: Proxy chaining mainly changes the network exit and forwarding path. It does not change the browser environment, TLS characteristics, or request behavior. Websites may still evaluate requests using multiple network and client-side signals.
▸ Browser environment signals: Canvas, WebGL, WebRTC leaks, and consistency between the time zone and language settings.
▸ Request behavior: Request frequency, URL patterns, interaction patterns, and other behavioral signals.
How to Configure a Proxy Chain More Effectively
1. Reduce unnecessary hops: Identify the purpose of each hop and remove any that are not needed.
2. Define the final hop: The exit node determines the address seen by the target website. Choose the IP type and location based on your business needs.
3. Check for leaks: Check whether DNS, IPv6, or WebRTC traffic bypasses the proxy chain.
4. Keep the environment consistent: Keep the exit IP's location reasonably consistent with the client's time zone and language settings to avoid obvious discrepancies.
Frequently Asked Questions
Q1: Does using a proxy chain significantly reduce network speed?
It can. More proxy hops usually result in higher network latency because requests have to be relayed through multiple nodes.
Proxy chains are better suited to scenarios that require a specific network path. They are generally not ideal for large file downloads or real-time video streaming.
Q2: Can a data center IP and a static residential IP be combined in the same proxy chain?
Yes, but whether this setup is suitable depends on the proxy services and network requirements. A common approach is to use a data center proxy as the front-end node and a static residential IP as the final exit, combining connection performance with a residential network exit.
However, adding another proxy hop also increases latency and potential points of failure. There is no need to add an extra hop simply for the sake of having one.
Q3: Do I still need browser environment isolation after setting up a proxy chain?
Not necessarily. It depends on the business use case and platform requirements. A proxy chain manages the network path, while the browser environment affects client-side signals. They address different aspects of a connection.
To learn more about global proxy IP selection, static residential IP deployment, and multi-environment access solutions, visit the IPDEEP website for more information.